
Building the Global Brand
ThreatBlock exists because a degree teaches you about cybersecurity. It rarely teaches you to do it. We take learners from traditional academics to real-world capability: real infrastructure, real tooling, real adversary tradecraft.
From Lecture Halls to Live Targets
Most training stops at slides and multiple-choice exams. Ours starts where they end. Every course is built around infrastructure shaped like the real thing: networks you scan, applications you exploit, clouds you defend. Because employers don’t hire people who watched; they hire people who did.
Taught From a Working Red Team
Our instructors are practitioners first. The techniques you learn on Tuesday were used on an engagement the week before. That is the difference between a curriculum and a craft, and it is why our alumni walk into interviews with stories, not certificates alone.
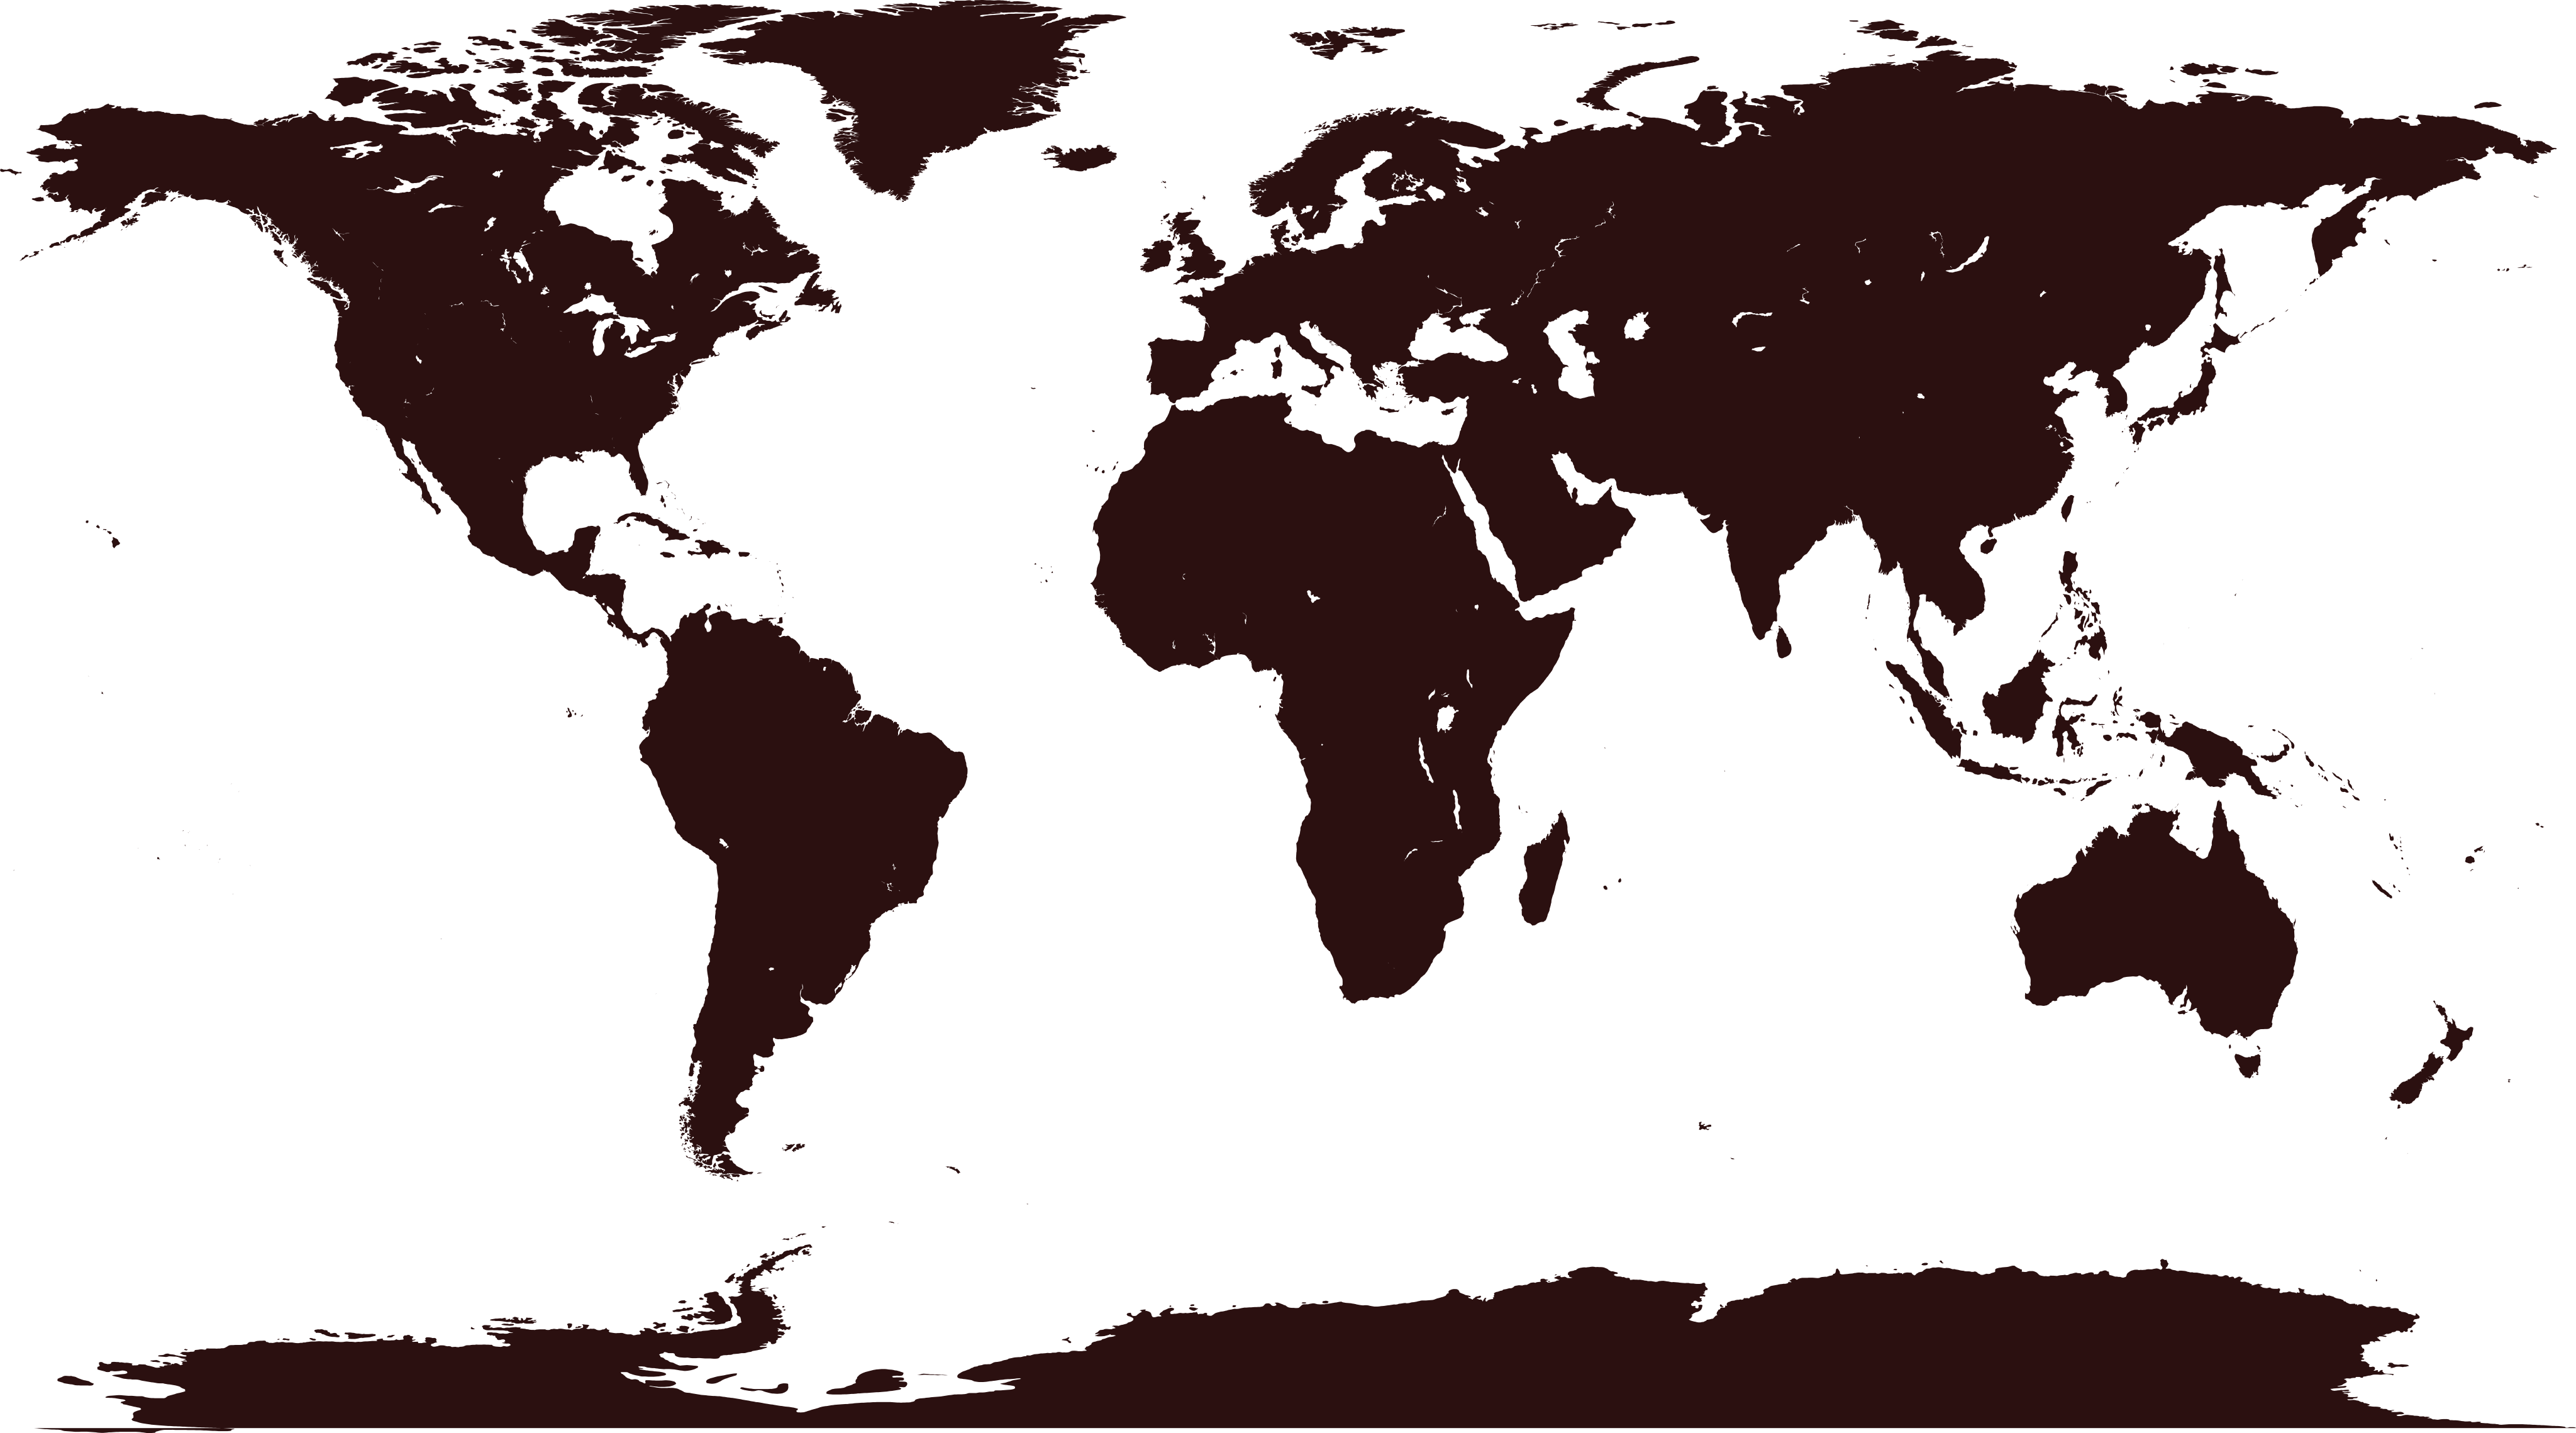
One Classroom. 27 Countries.
Every red dot is a live cohort. Students tune in from every timezone. Same labs, same instructors, same standard.
The Instructors. Real Faces, Real Engagements.
Our trainers hold the highest industry standards, including OSCP, CRTO, and CREST certifications, earned in the field, not just the exam hall.
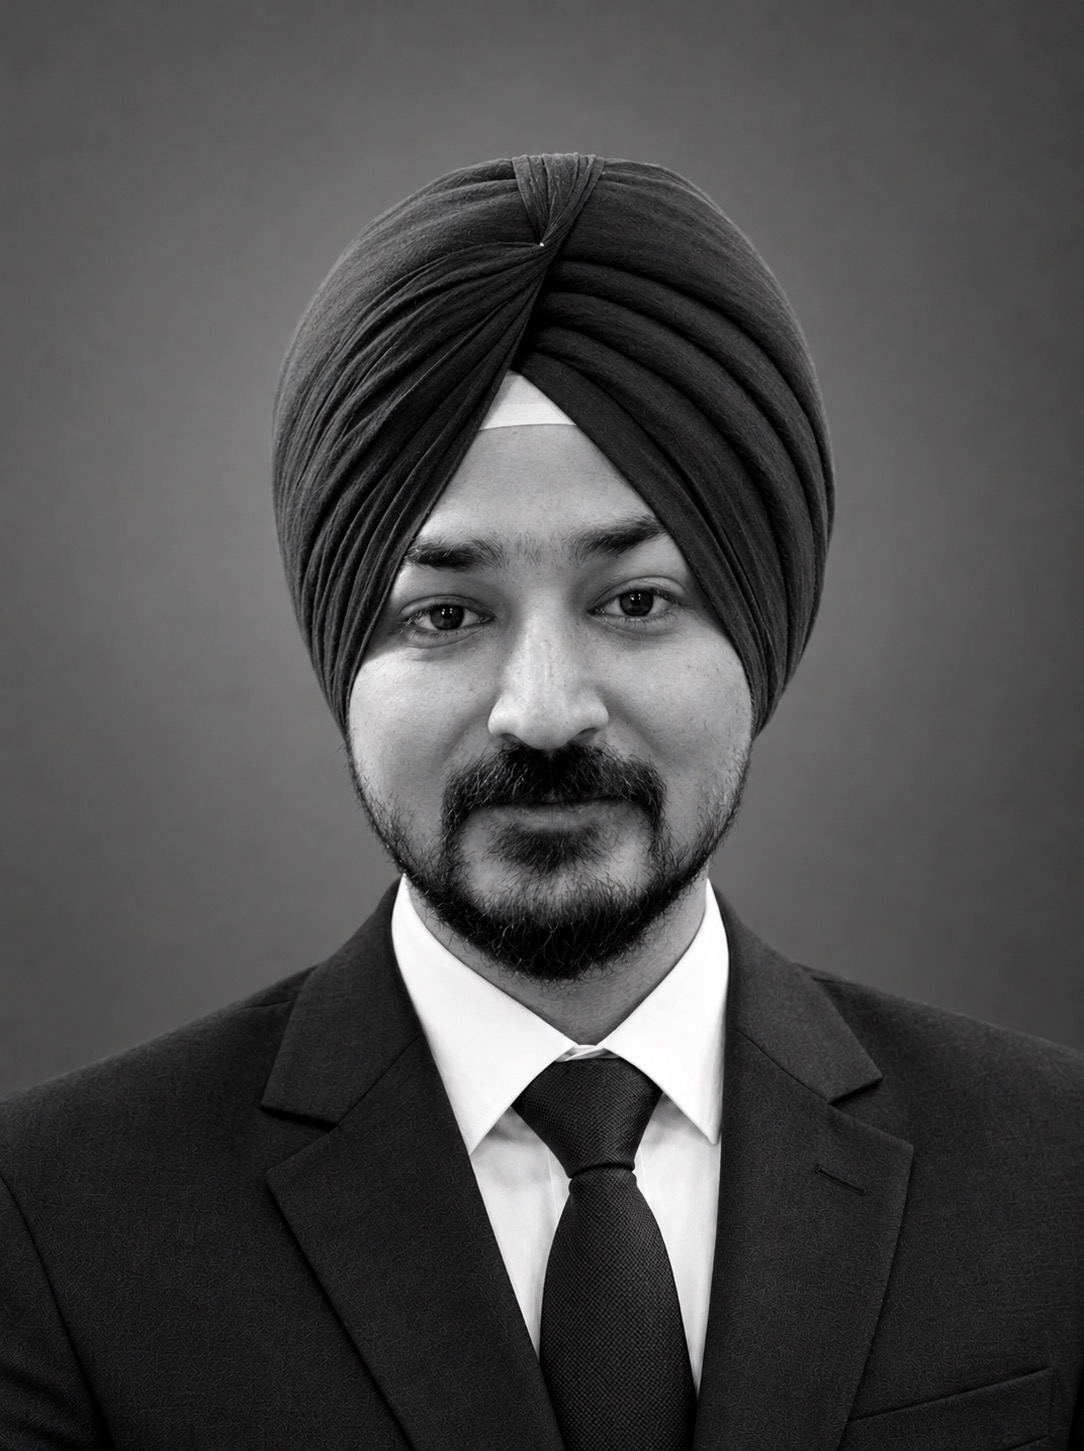
Gautam
11+ years of offensive security. Has led engagements against banks, telecoms and government infrastructure.
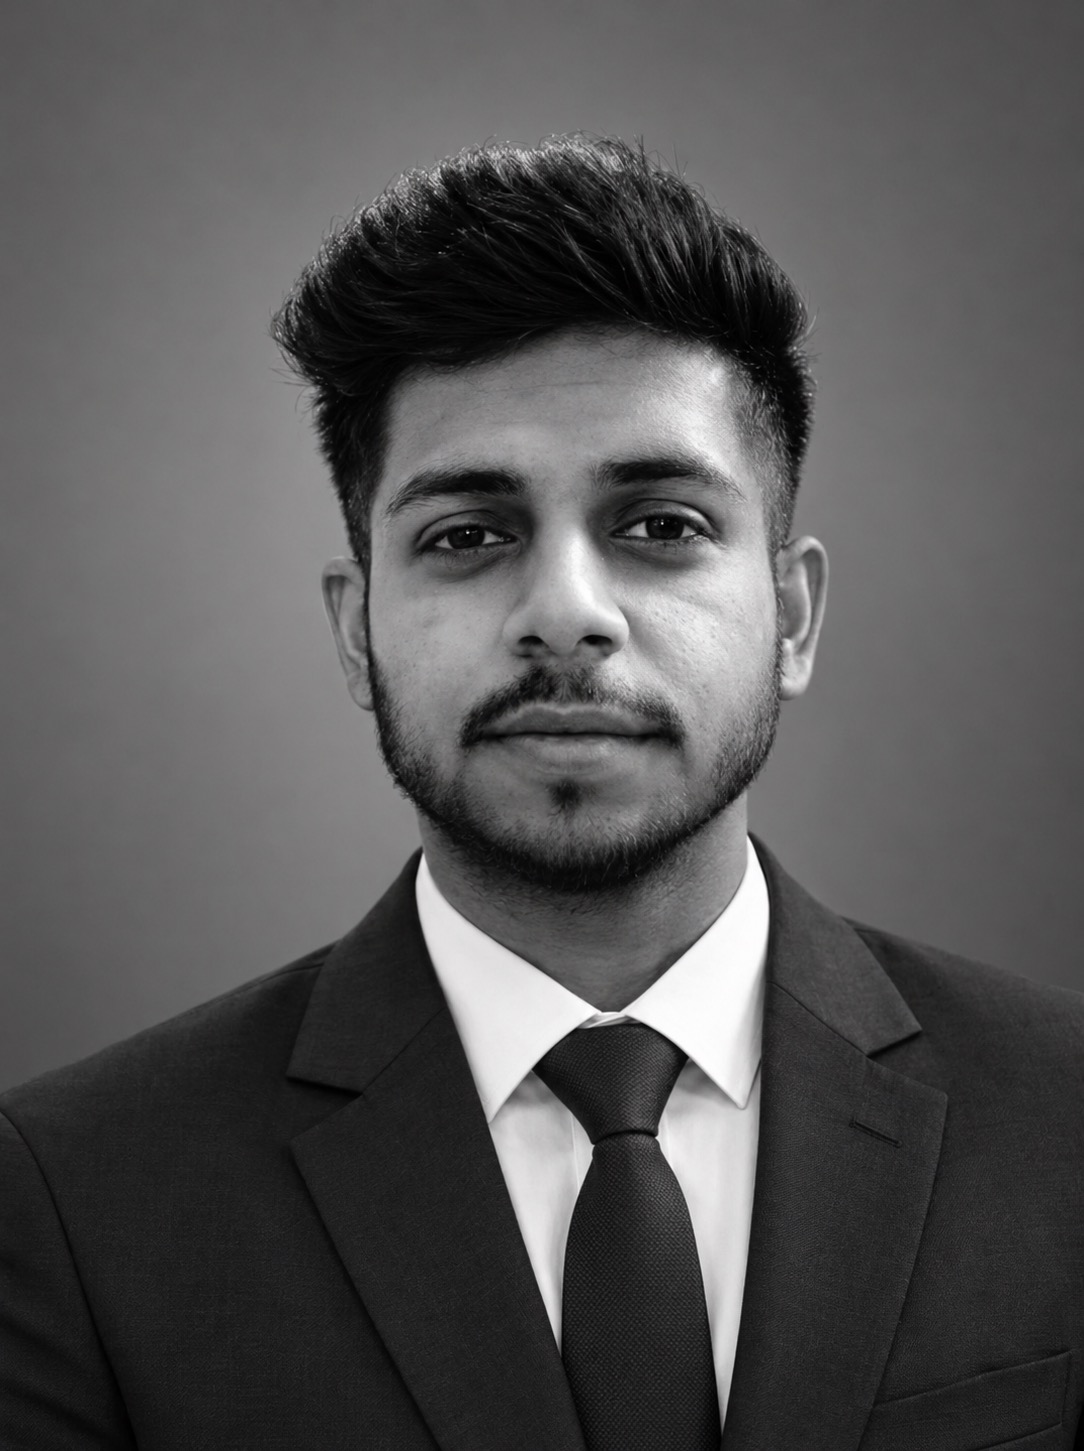
Manmeet
Former cloud incident responder. Teaches AWS attack and defense from cases she actually worked.
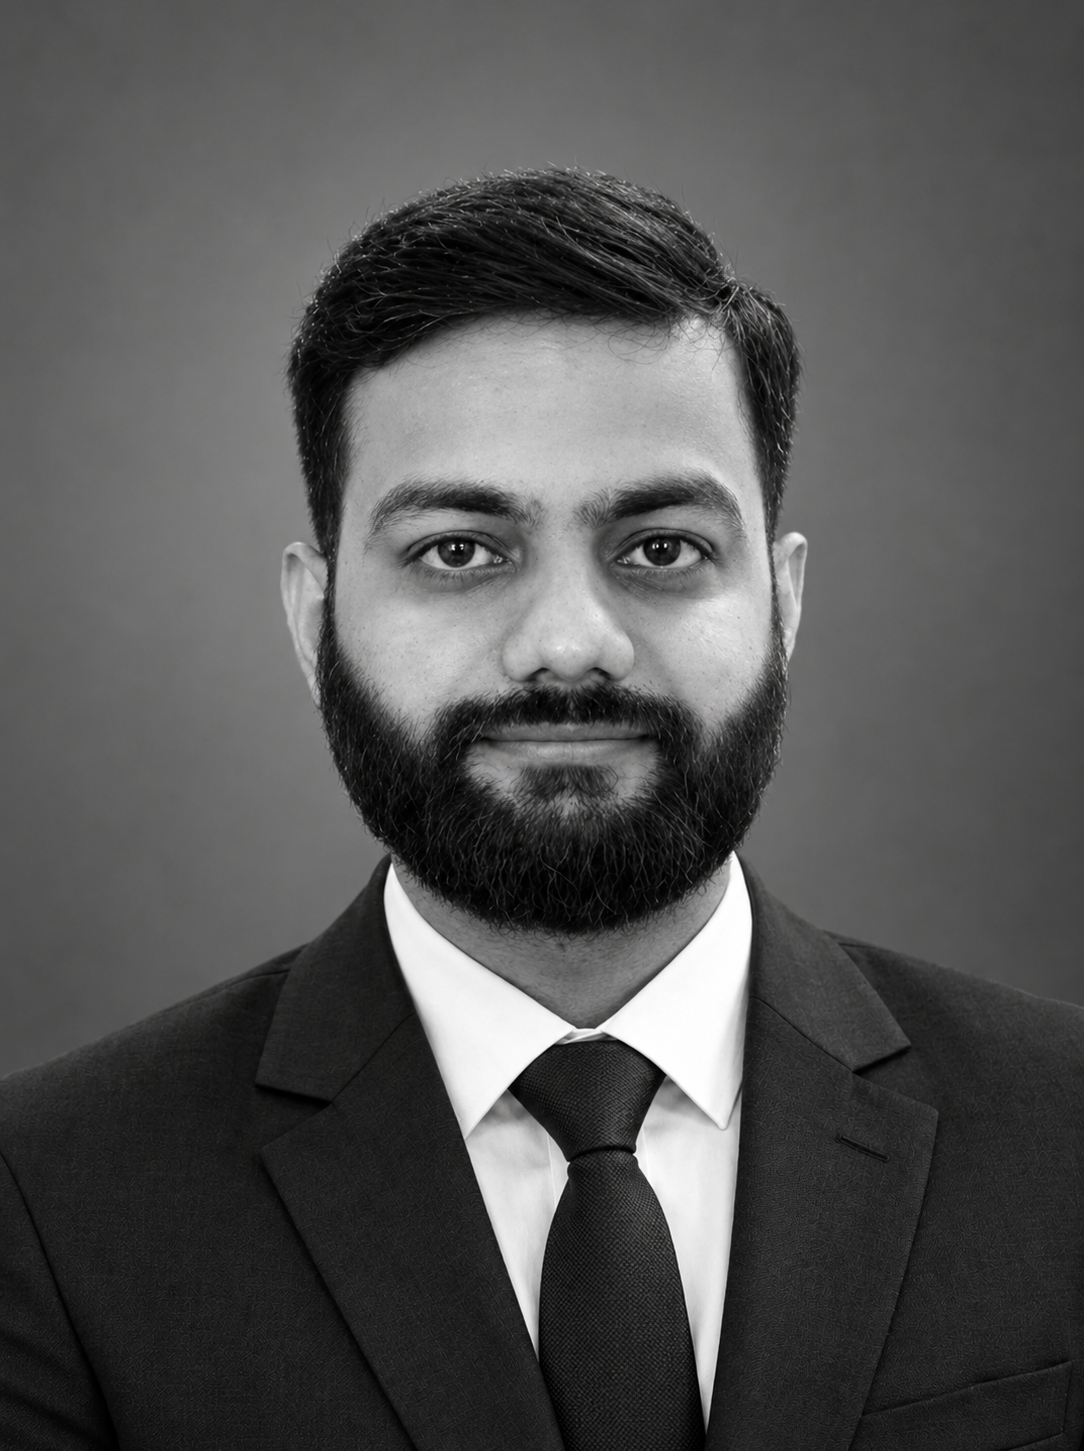
Samaksh
Builds the labs you break. Specialist in adversary tradecraft, C2 infrastructure and detection evasion research.
Ethical by Design
Every class runs in controlled, isolated lab environments built and owned by ThreatBlock. We teach authorized testing. Scoping, rules of engagement, and responsible disclosure are part of the syllabus, not an afterthought. Our students learn to break things legally, so they can defend them professionally.